


Cyber Resilience Act (CRA)
Preparing Industrial Networks for evolving EU cybersecurity requirements.
The EU Cyber Resilience Act (CRA), Regulation (EU) 2024/2847, establishes mandatory cybersecurity requirements for products with digital elements placed on the EU market. EtherWAN is preparing its industrial Ethernet products and lifecycle processes through IEC 62443-certified secure development, independently certified product-security capabilities, coordinated vulnerability response, and continued work on risk assessment, technical documentation, support periods, secure updates, and regulatory reporting.
Core cybersecurity obligations for manufacturers
The CRA establishes horizontal cybersecurity requirements for products with digital elements made available on the EU market. Manufacturers must address product properties, vulnerability handling, documentation, reporting, and conformity obligations.
Secure by Design and by Default
Cybersecurity risks must be considered during design, development, production, and delivery, with secure default configurations.
Risk and Vulnerability Management
Manufacturers must identify, document, monitor, prioritize, and remediate vulnerabilities, including risks in third-party components.
Security Updates and Lifecycle Support
Manufacturers must define and communicate a support period that reflects expected product use, during which vulnerabilities are handled and security updates are made available.
Documentation, Conformity and Reporting
Technical documentation, conformity assessment, CE marking, user information, and time-bound regulatory reporting are central obligations.
CRA timeline and key deadlines
The regulation is being implemented in phases, allowing manufacturers time to adapt products, processes, documentation, and vulnerability reporting mechanisms.
Preparation for phased CRA obligations begins.
Notification rules for assessment bodies apply.
Reporting begins for exploited vulnerabilities and severe incidents.
Most requirements apply to in-scope products.
Cybersecurity foundations already in place
EtherWAN has integrated cybersecurity into product development and lifecycle management through an IEC 62443-4-1 certified secure development process, IEC 62443-4-2 certified industrial Ethernet switches, and structured product vulnerability response. These product-security foundations are supported by an ISO/IEC 27001:2022 certified information security management system.
Certified Secure Development
IEC 62443-4-1 certified processes incorporate cybersecurity across planning, requirements, design, implementation, verification, release, maintenance, and incident response.
Learn about IEC 62443-4-1Certified Product Security Capabilities
Selected EtherWAN industrial Ethernet switch families are independently certified to IEC 62443-4-2 for defined component-level security capabilities.
Explore certified productsCoordinated Vulnerability Response
EtherWAN’s PSIRT provides a structured channel for receiving, investigating, coordinating, and communicating product security vulnerabilities.
Visit EtherWAN PSIRTBuilding blocks for CRA readiness
Building on its certified development, product-security, and vulnerability-response foundations, EtherWAN’s CRA preparation focuses on the product-specific work needed for implementation.
Product Cybersecurity Risk Assessment
Preparation focuses on product-specific assessments covering intended purpose, reasonably foreseeable use, operating environments, assets to be protected, and applicable essential cybersecurity requirements.
Component and SBOM Governance
Preparation includes strengthening component records, third-party dependency oversight, vulnerability monitoring, and software bill of materials practices.
Support Period and Secure Updates
Preparation includes defining product support periods, secure update mechanisms, remediation practices, and customer-facing information that reflect expected product use and lifecycle obligations.
CRA Reporting Workflow
Preparation focuses on escalation, assessment, notification, and evidence-retention workflows for actively exploited vulnerabilities and severe incidents affecting product security.
Technical Documentation and Conformity Preparation
Following the European Commission’s published CRA guidance and ongoing standardisation work, preparation includes product technical documentation, secure-use information, conformity evidence, and product-specific assessment planning.
Extend CRA readiness into your branded product portfolio
For OEM and private-label projects, product identity, market roles, technical documentation, vulnerability response, update responsibilities, and lifecycle support should be clearly defined between EtherWAN and the brand owner.
EtherWAN combines Taiwan-based design and manufacturing, IEC 62443-certified development, certified industrial networking platforms, and established OEM services to coordinate available product information, technical evidence, vulnerability handling, updates, and lifecycle communication according to the agreed project scope.
Security-Oriented Product Selection
EtherWAN can help partners evaluate industrial Ethernet platforms according to application, performance, environmental, and cybersecurity requirements, including IEC 62443-4-2 certified options where appropriate.
Private-Label Content Alignment
Device labels, packaging, manuals, product cases, and mylar can be customized to align with the partner’s brand. Project-specific secure-use and product information can be coordinated as part of the documentation process.
Certification and Technical Evidence
Available certificate copies, assessment reports, test information, and IEC 62443 evidence can support customer evaluation and technical-file preparation, subject to the selected product and agreed project scope.
Vulnerability Response Coordination
EtherWAN’s PSIRT foundation can support project-specific coordination for vulnerability intake, assessment, security communication, mitigation, and remediation between EtherWAN and the private-label partner, while CRA reporting responsibility follows the applicable market role.
Lifecycle and Change Communication
OEM programs can define how product changes, available security updates, support-period information, and end-of-life notices are communicated, helping each party maintain its agreed lifecycle and customer-facing responsibilities.
Manufacturing and After-Sales Continuity
In-house design and manufacturing in Taiwan, production management, product testing, delivery coordination, and technical after-sales support provide a stable operational foundation for long-term OEM programs.
IEC 62443-4-2 certified industrial Ethernet switches
Choose secure industrial connectivity for high-bandwidth backbones, high-power PoE, power utility networks, segmented OT environments, and hardened infrastructure deployments.
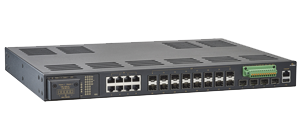
IG5 L Rack Series
IEC 61850-3 / IEEE 1613 industrial managed switch for power and substation networks.
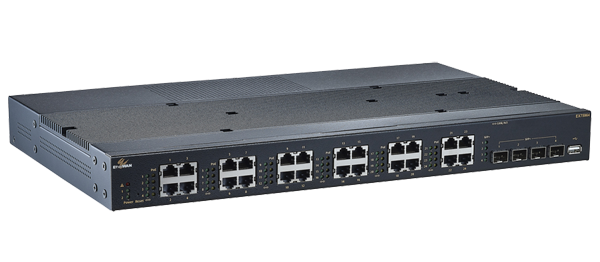
EX75900 Series
Hardened rackmount PoE platform with up to 90 W per port and 720 W total PoE budget.
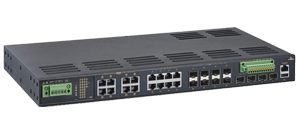
IG5 SV Series
Short-depth substation switch with PoE, 10G uplinks, and hardened environmental design.
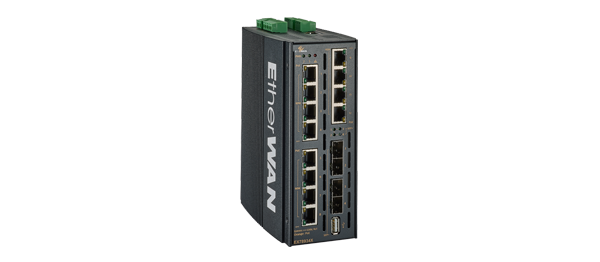
EX78900X Series
Industrial IEEE 802.3bt PoE switch with 12 Gigabit PoE ports and four 10G SFP+ uplinks.
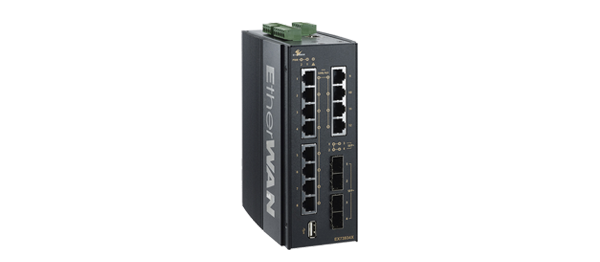
EX73900X Series
Hardened managed Gigabit switch with four 10G SFP+ uplinks for resilient OT backbones.
EX78900E Series
Hardened managed PoE switches for flexible industrial access and edge connectivity.
Understanding CRA readiness
The following information provides a general overview. Product-specific applicability and conformity routes should be evaluated based on the final use case and current regulatory guidance.
What is the EU Cyber Resilience Act?
The Cyber Resilience Act is Regulation (EU) 2024/2847. It establishes horizontal cybersecurity requirements for products with digital elements placed on the European Union market, covering product properties and vulnerability handling throughout the lifecycle.
Does the CRA apply to industrial Ethernet switches?
Industrial Ethernet switches may fall within the scope of the CRA when they are made available on the EU market and include a direct or indirect logical or physical data connection. Product classification and the applicable conformity-assessment route depend on the product’s core functionality, intended use, and current regulatory guidance.
When will the CRA requirements apply?
The CRA entered into force on December 10, 2024. Reporting obligations for actively exploited vulnerabilities and severe product-security incidents apply from September 11, 2026. Most other requirements apply from December 11, 2027, subject to the CRA’s transitional provisions.
What must manufacturers report under the CRA?
From September 11, 2026, manufacturers must report actively exploited vulnerabilities and severe incidents affecting product security. The CRA requires an early warning within 24 hours of awareness, followed by a fuller notification within 72 hours and a final report within the applicable deadline.
Does IEC 62443 certification automatically mean CRA compliance?
No. IEC 62443 provides an important technical and process foundation, but CRA conformity also depends on product scope and classification, cybersecurity risk assessment, technical documentation, vulnerability handling, regulatory reporting, applicable harmonised standards, and the required conformity assessment procedure.
Who is responsible for CRA obligations in an OEM or private-label project?
Responsibilities depend on how the product is branded, modified, and placed on the EU market. A company that markets a product under its own name or trademark may be considered the manufacturer under the CRA. The applicable roles and responsibilities should therefore be defined for each project.
What does the CRA support period mean?
Manufacturers must define and communicate a support period that reflects the product’s expected use. During that period, product vulnerabilities must be handled effectively and security updates must be made available in accordance with the applicable CRA requirements.
How does EtherWAN address product vulnerabilities?
EtherWAN operates a Product Security Incident Response Team to receive vulnerability reports and coordinate investigation, internal response, communication, mitigation, and publication of security advisories where appropriate.
How is EtherWAN preparing for the CRA?
EtherWAN’s CRA preparation builds on IEC 62443-4-1 certified secure development, IEC 62443-4-2 certified product capabilities, PSIRT vulnerability response, and ISO/IEC 27001:2022 information security management. Current preparation focuses on product risk assessment, component and SBOM governance, support periods, secure updates, reporting workflows, and technical documentation.
Build resilient industrial networks for evolving cybersecurity requirements
Explore EtherWAN’s IEC 62443-certified development foundation and industrial Ethernet solutions for secure, reliable, and lifecycle-ready OT connectivity.


